> For the complete documentation index, see [llms.txt](https://docs.prismacloud.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.prismacloud.io/admin-guide/33/vulnerability-management/search-cves.md).
# CVE Viewer
Common Vulnerabilities and Exposures (CVE) is a system for referencing publicly known vulnerabilities by identifiers. The goal of the system is to make it easier to share vulnerability data across stakeholders, including software vendors, tool vendors, security practitioners, and end users.
A *CVE entry* describes a specific known vulnerability. Each CVE entry has an identifier, such as CVE-2020-1234. A *CVE entry* is colloquially known as a *CVE*, and it’s security practitioner parlance for a publicly disclosed vulnerability.
## Search for a specific CVE
You can determine if Prisma Cloud offers coverage for a specific CVE by using the search interface in Console. The CVE ID syntax is:
```
CVE-YYYY-NNNN
```
Where:
| CVE | CVE-ID prefix. |
| ---- | ---------------------------------------------------------------------------------------- |
| YYYY | Calendar year. |
| NNNN | Numeric digits. This field has a variable length, but the minimum length is four digits. |
To search for a specific vulnerability:
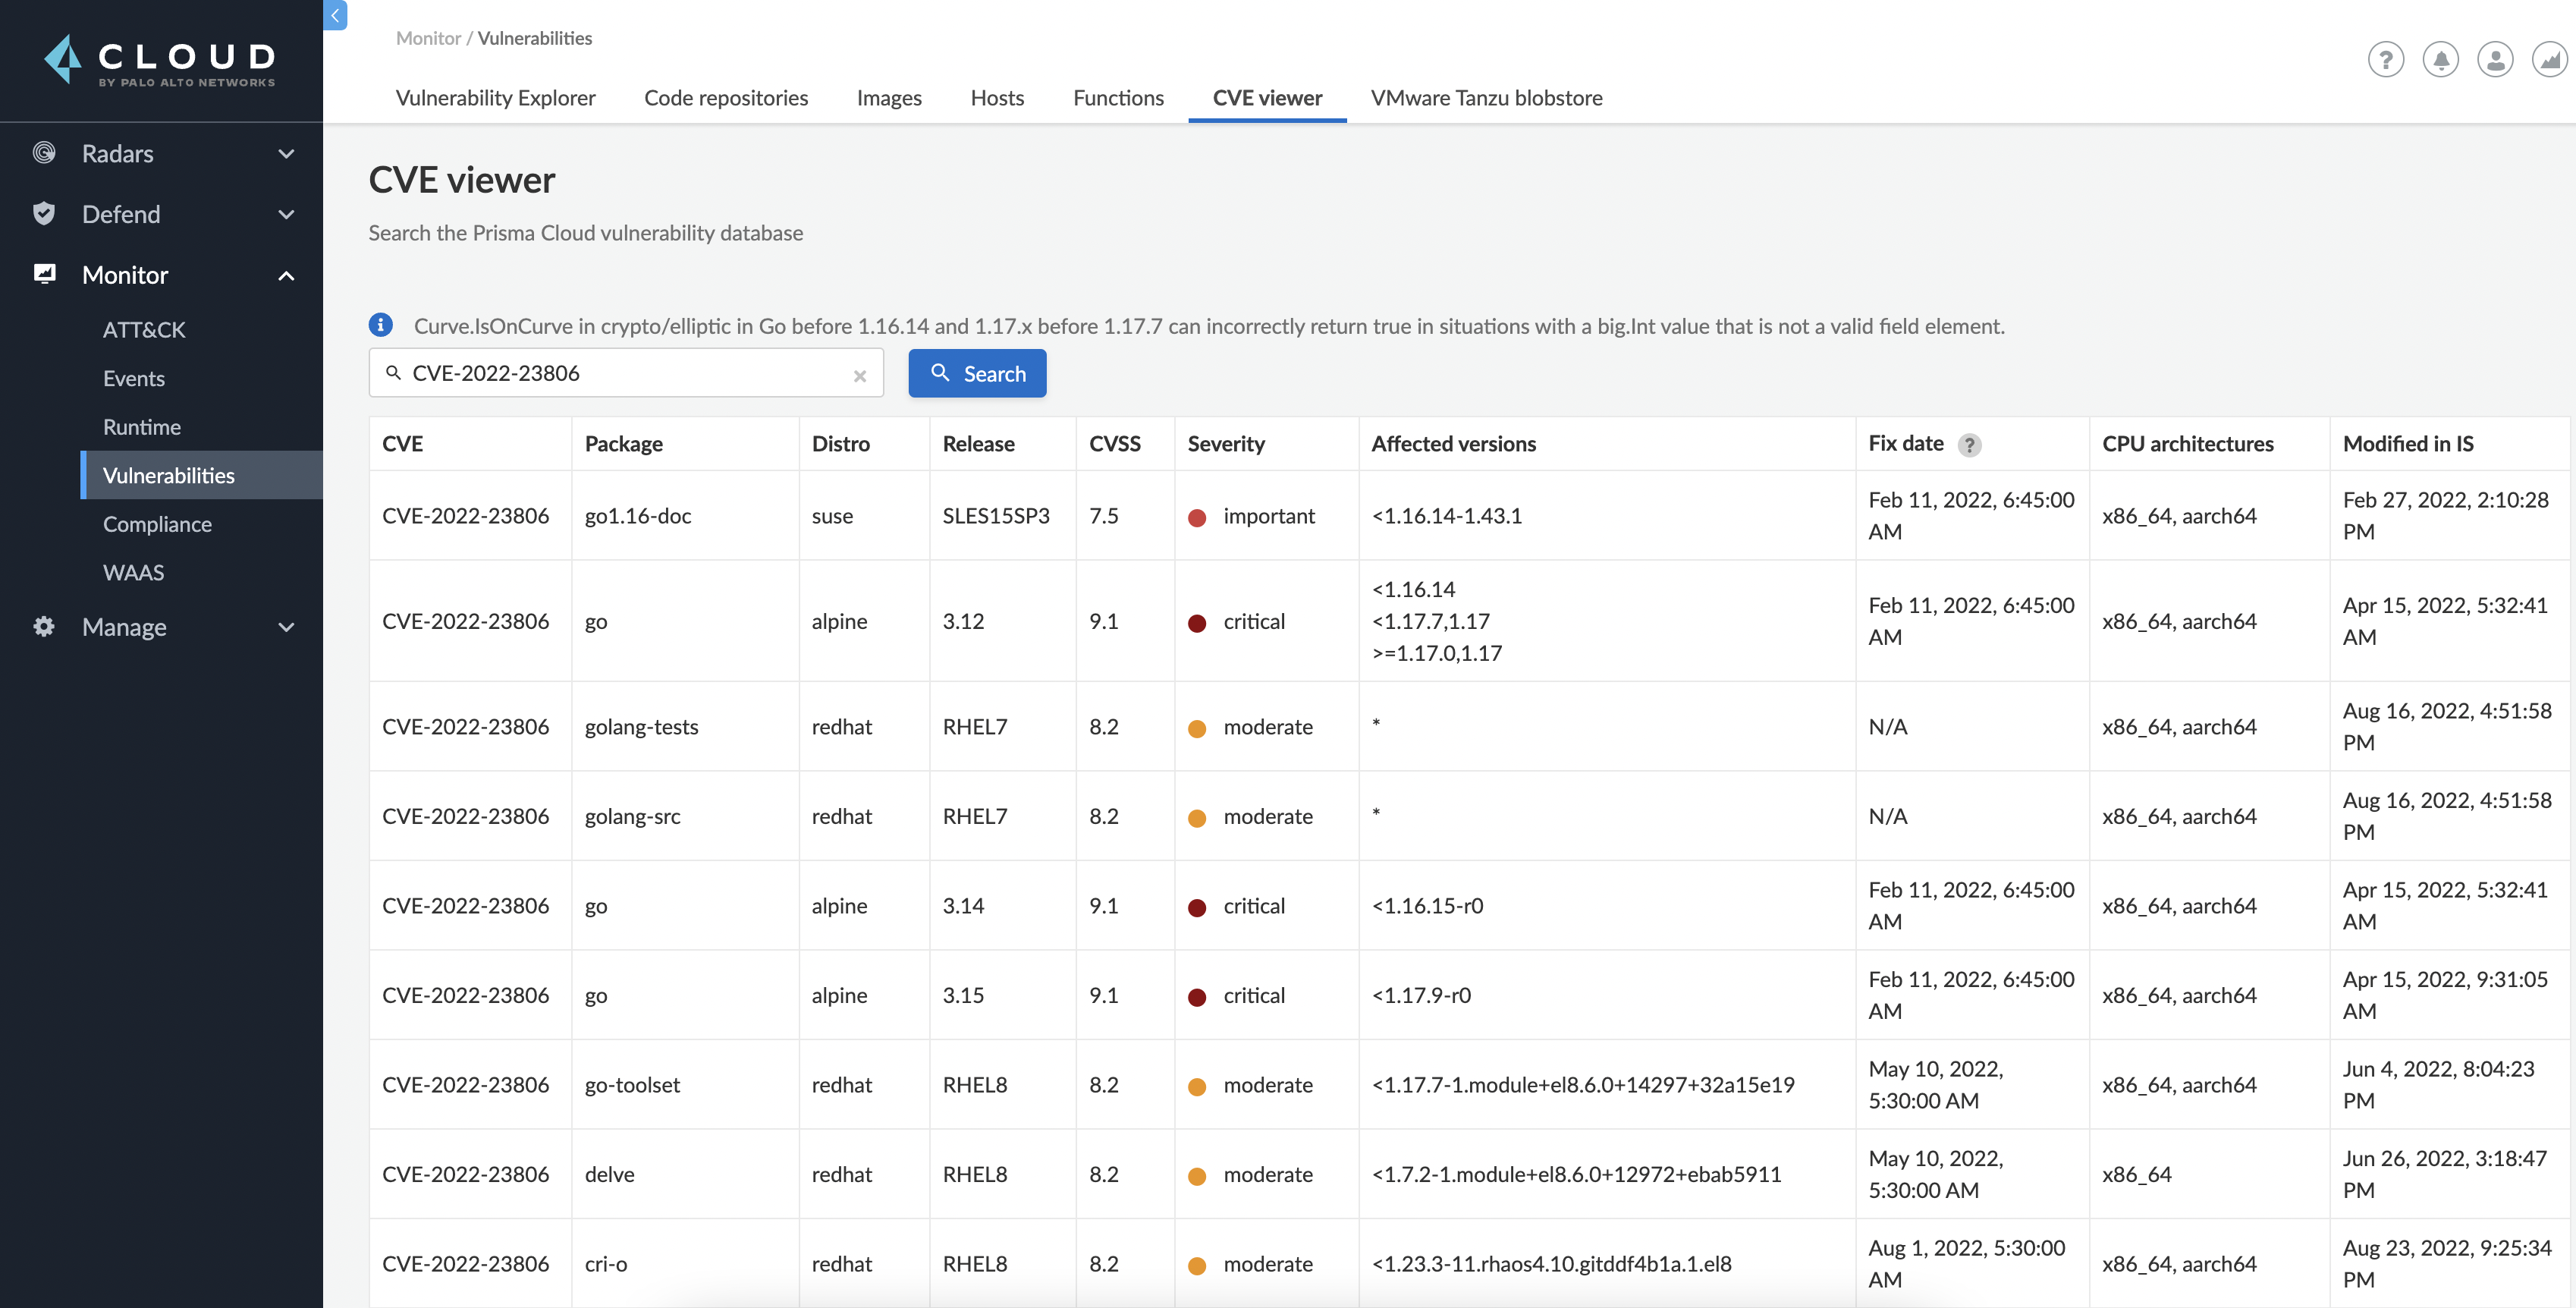
1. Open Console, then go to **Monitor > Vulnerabilities > CVE Viewer**.
2. Enter a CVE ID in the search box.
For example, enter **CVE-2022-23806**.
If Prisma Cloud has coverage for the queried vulnerability, details are listed in the results table.
## Allow a CVE
Allowing CVEs is done directly as a policy.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.prismacloud.io/admin-guide/33/vulnerability-management/search-cves.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.