> For the complete documentation index, see [llms.txt](https://docs.prismacloud.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.prismacloud.io/admin-guide/runtime-defense/incident-types/backdoor-ssh-access.md).
# Backdoor SSH access
Backdoors give attackers a way to bypass normal authentication systems, and are used to secure remote access to a system.
Backdoor SSH access incidents indicate that an attacker might have changed the configuration of a resource to enable remote access to the resource.
## Investigation
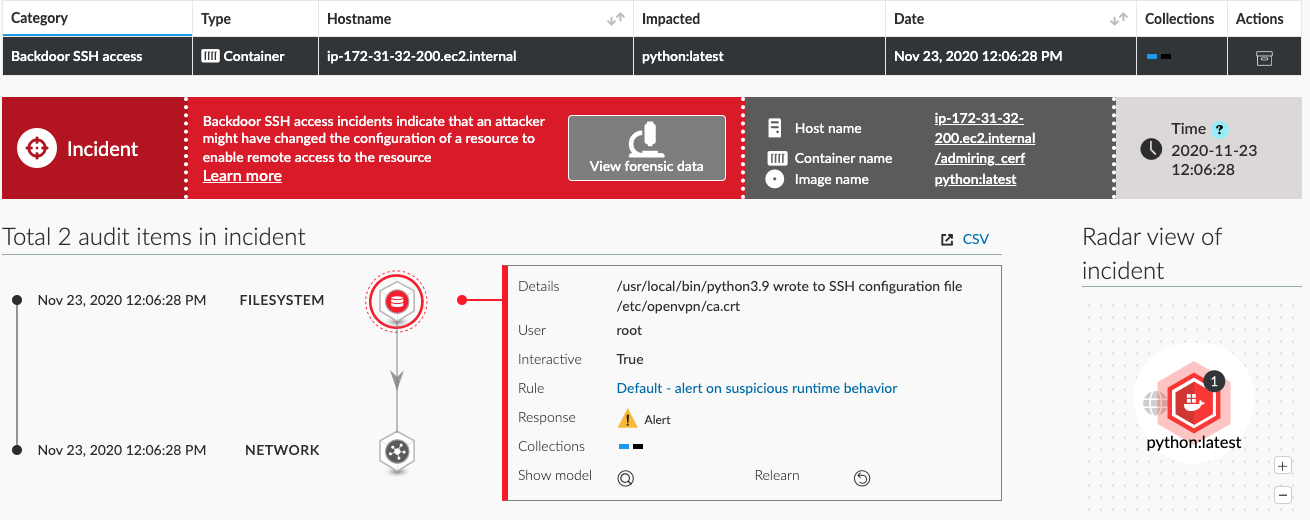
In the following incident, you can see two audits. The first audit is a file system event that shows a new certificate was created in */etc/openvpn*. An attacker could use this certificate for follow-on access to the container.
The first step in an investigation is to validate that the changes represent a bona fide security incident. In this example, it’s unlikely that a change in the ca cert file is a valid one, but it might not always be so clear.
After validating that this is a security incident, the next step is determining how an attacker was able to modify the system configuration. This would, generally, be a post-compromise approach to maintain access to the compromised systems. Check Incident Explorer for other potentially related incidents. Review additional runtime audits for the source to see if there are other clues.
Review access to the container and ensure that accesses weren’t subsequently used for further access to systems and data.
## Mitigation
A full mitigation strategy for this incident begins with resolving the issues that allowed the attacker to modify the system configuration.
Ensure that compliance benchmarks are appropriately applied to the affected resources. For example, if the critical file systems in the container are mounted read-only, it will be more difficult for an attacker to change a configuration to their advantage.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.prismacloud.io/admin-guide/runtime-defense/incident-types/backdoor-ssh-access.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.