> For the complete documentation index, see [llms.txt](https://docs.prismacloud.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.prismacloud.io/admin-guide/web-application-and-api-security-waas/unprotected-web-apps.md).
# Unprotected web apps
Prisma Cloud scans your environment for containers and hosts that run web apps and reports any that aren’t protected by WAAS.
During the scan, Prisma Cloud detects HTTP servers listening on exposed ports and flags them if they are not protected by WAAS.
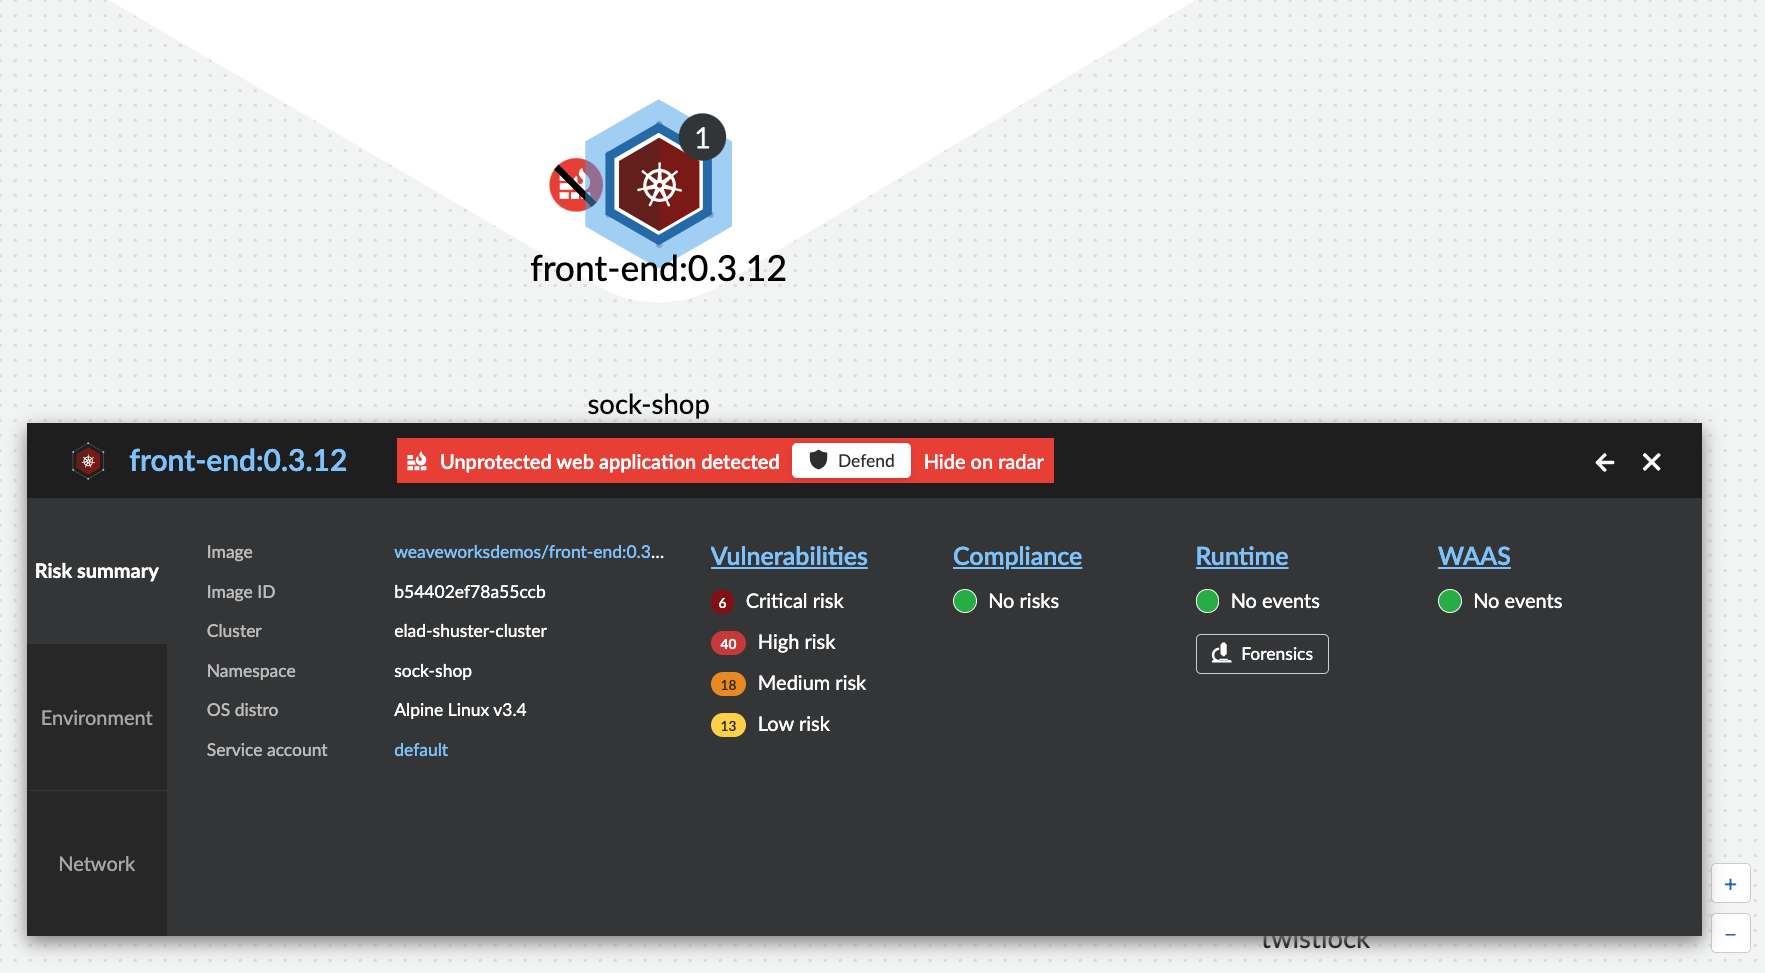
Unprotected web apps are flagged on the radar view and are also listed in **Monitor > WAAS > Unprotected web apps**.
The following screenshot shows how Radar shows an unprotected web app:
## Report for unprotected web apps
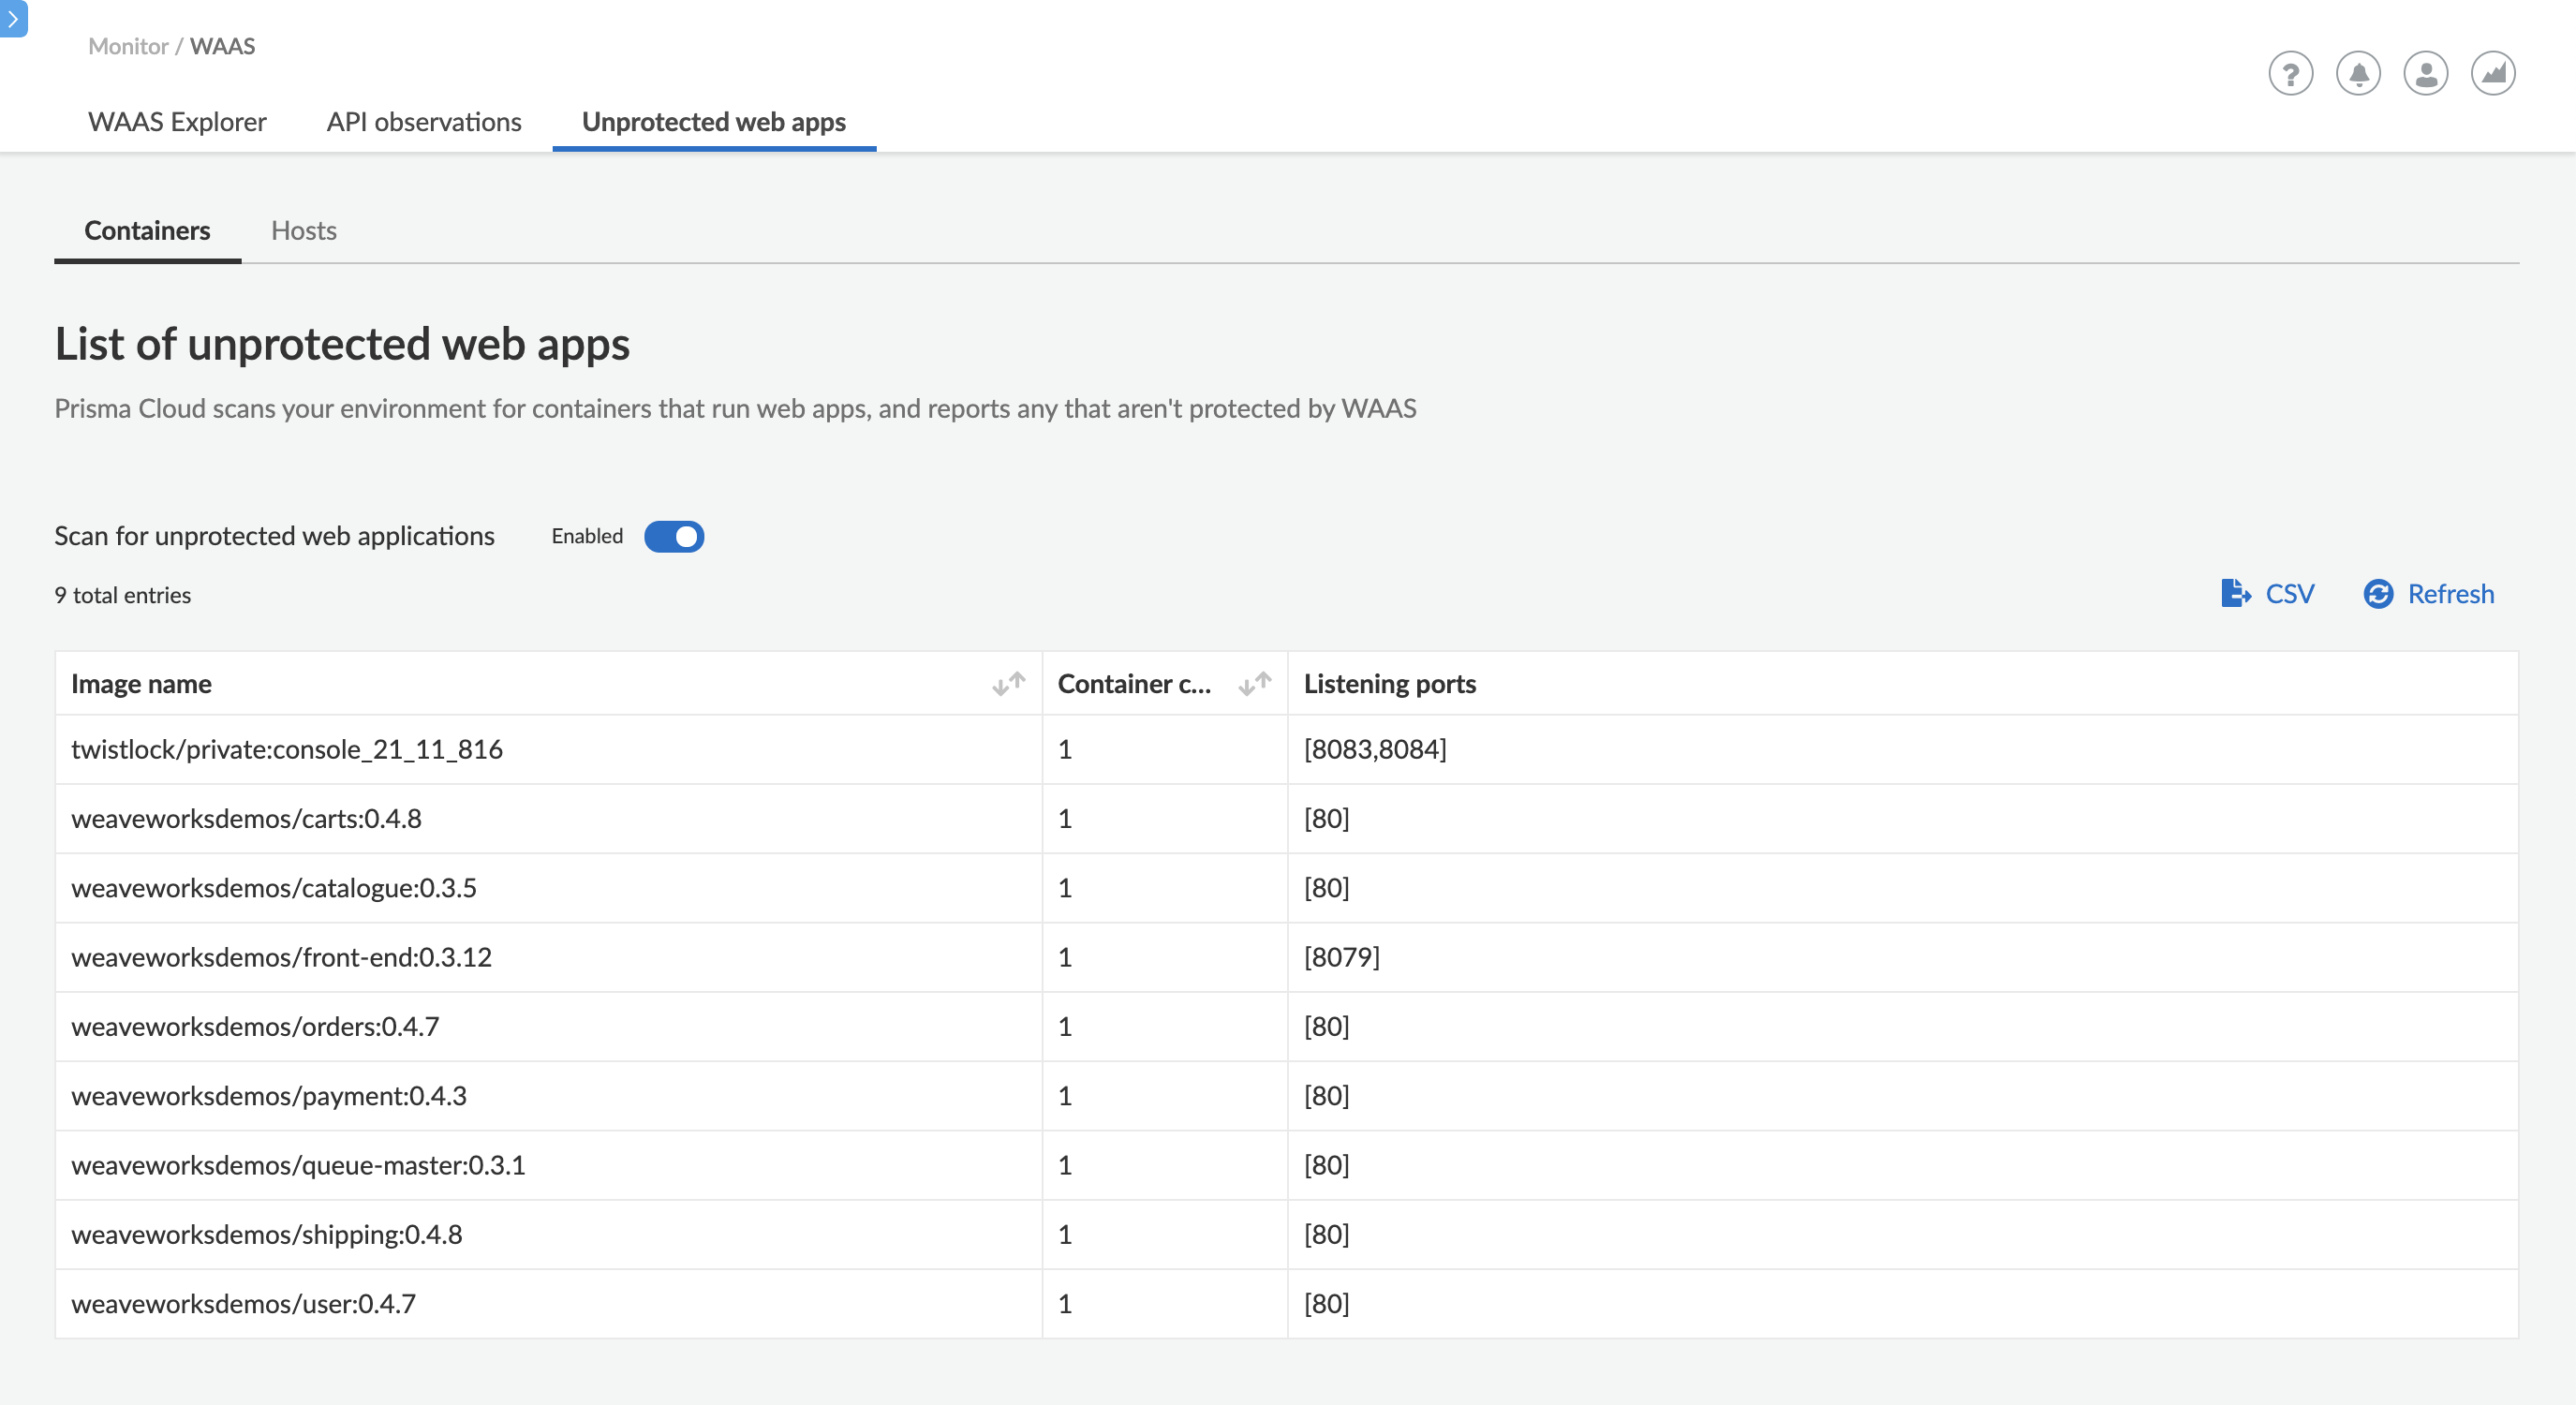
The following screenshot shows how unprotected web apps are reported in **Monitor > WAAS > Unprotected web apps**:
In the `Containers` tab, the report lists the images containing unprotected web apps, the number of containers running those images, and the ports exposed in the running containers.
In the `Hosts` tab, the report lists the hosts on which unprotected web apps are running, the number of processes running those apps, process names and the ports exposed in the hosts.
This information can be used when adding new WAAS rules to protect containers and hosts.
Above the table is the date of the latest scan. The report can be refreshed by clicking the refresh button.
Users can export the list in CSV format. The CSV file has the following fields:
* **Containers** - Image, Host, Container, ID, Listening ports
* **Hosts** - ID, Unprotected processes
## Filtered processes
The following list of processes is not included in the WAAS unprotected web apps detections:
**Kubernetes/Docker**
* coredns
* kube-proxy
* docker
* docker-proxy
* kubelet
* openshift
* dcos-metris
* dcos-metris-agent
* containerd
**Databases**
* mysql
* mysqld
* mongod
* postgres
* influxd
* redis-server
* asd
* rethinkdb
**Proxies**
* haproxy
* envoy
* squid
* traefik
**SSH binaries**
* sshd
* ssh
**WAAS proxy process**
* defender
## Disabling scans for unprotected web apps
By setting the `Scan for unprotected web applications` toggle to the **Disabled** position, users are able to disable periodic scanning for unprotected web applications and APIs.
The toggle in either the `Containers` or `Hosts` tabs will disable scanning of containers and hosts simultaneously when disabled.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.prismacloud.io/admin-guide/web-application-and-api-security-waas/unprotected-web-apps.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.